Chinese Government-linked Cyber Threat Actors Combine Automated and Hands-on Hacking Tools to Steal Sensitive Data
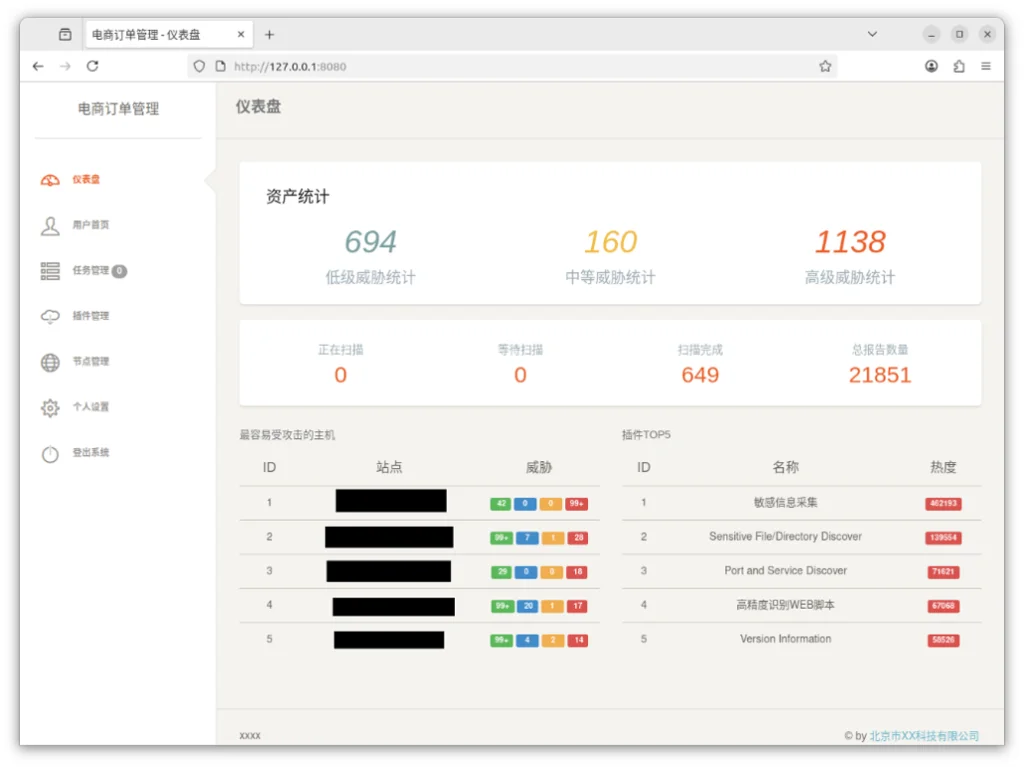
Chinese government-linked cyber threat actors, facilitated by Integrity Technology Group, are employing a sophisticated blend of automated tools and hands-on hacking techniques. They systematically scan for vulnerabilities in organizations globally, including critical US infrastructure. Their methods involve exploiting vulnerabilities through techniques like cross-site scripting and password spraying attacks, particularly targeting Microsoft Exchange servers. To maintain access, these threat actors establish persistence using VPN software and then exfiltrate sensitive data, such as emails and credentials, through custom scripts. Organizations are strongly advised to implement robust security measures to counter these threats. Key mitigation strategies include disabling unused services and ports on their networks. It is crucial to sanitize web application inputs to prevent injection attacks and to enforce multi-factor authentication for all services. Promptly applying software patches remains a fundamental defense against potential compromises. These combined efforts aim to protect sensitive data from exploitation by these persistent attackers.