Google Cloud Blog
Follow
ARMORY CASTLE Exploits BeyondTrust
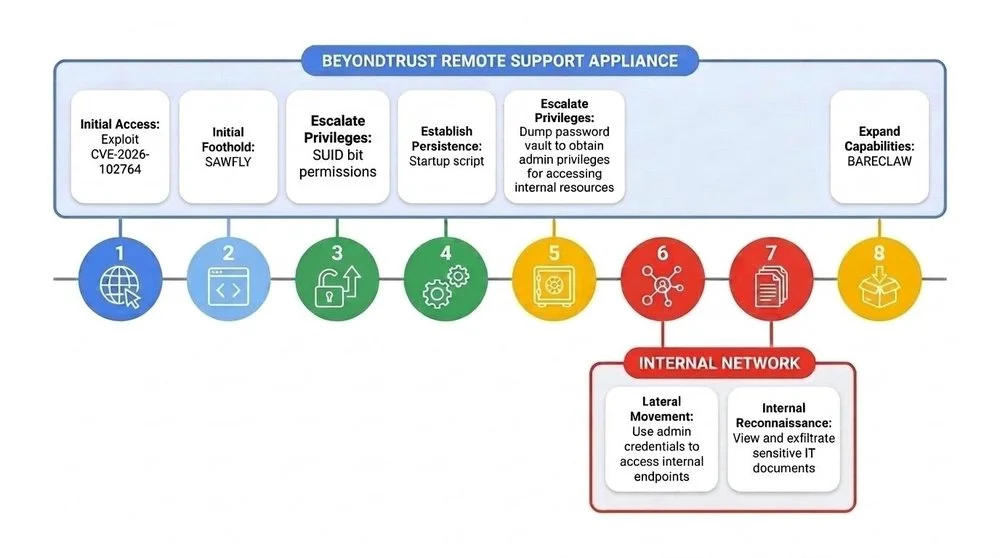
BeyondTrust disclosed a vulnerability, CVE-2026-102764, in its Remote Support appliances, allowing arbitrary file uploads. Mandiant discovered suspected PRC-nexus actor ARMORY CASTLE exploited this as a zero-day in late August 2026. The actor established a foothold using a custom PHP webshell called SAWFLY, which communicated via encrypted C2. Privilege escalation to root was achieved by manipulating SUID permissions on a system binary. ARMORY CASTLE then harvested credentials using the proprietary bt-secrets CLI utility. For long-term persistence, they modified appliance configuration templates to grant passwordless root access to a service account. The threat actor actively deleted logs to evade detection and hinder forensic analysis. They also abused compromised administrator credentials to gain access to the BeyondTrust web portal. Furthermore, ARMORY CASTLE modified user permissions to permanently gain unrestricted remote access to downstream systems. Finally, they used a custom tunneler named BARECLAW to exfiltrate data and move laterally within the network.