Trail of Bits Blog
Follow
Don't let TEEs break your MPC
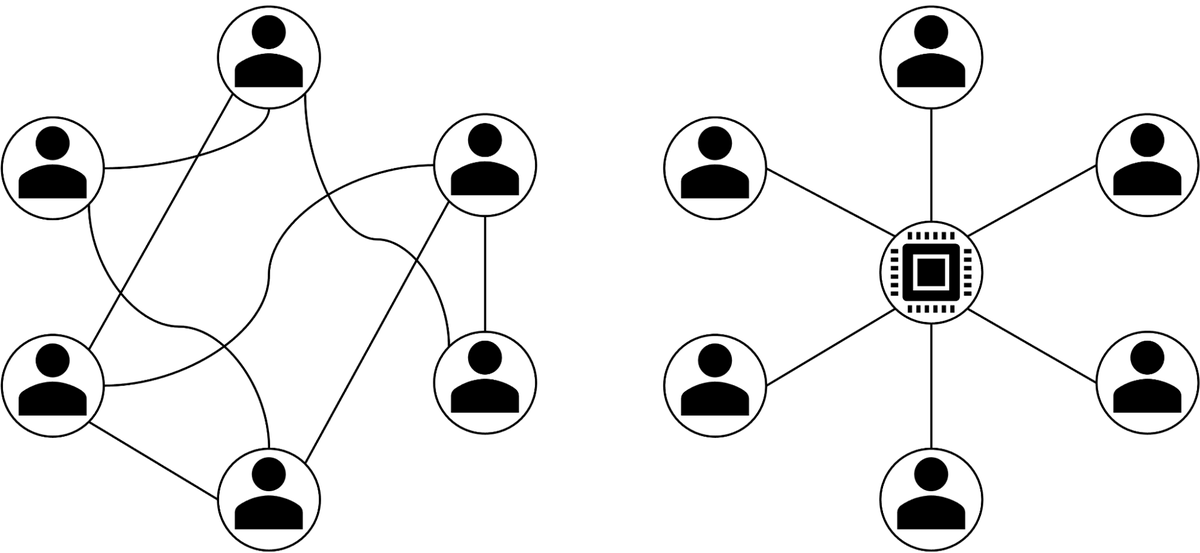
Threshold signature schemes, a multi-party computation (MPC) method allowing joint signing without a single key, are increasingly used within Trusted Execution Environments (TEEs) for enhanced security. MPC distributes trust across parties, while TEEs root trust in hardware. However, running MPC in a TEE without considering an untrusted host can introduce vulnerabilities, such as a malicious host rolling back filesystem state, leading to private key share disclosure.The combination is beneficial if TEEs are treated as a defense-in-depth layer, not a protocol substitute. This approach highlights TEE attestation's role in MPC deployments, common audit pitfalls, and best practices like strong attestation binding to MPC identities. MPC's security relies on participant behavior, with models like semi-honest (honest-but-curious) and malicious security. TEE attestation, if comprehensive, can elevate semi-honest protocols to provide malicious security guarantees against certain attacks.TEEs offer confidentiality, integrity, and attestation. Attestation, crucial for distributed systems, allows remote verification of code running in the TEE. The process involves the TEE signing cryptographic hashes of its state, forming a "quote," which remote parties verify. Verification necessitates checking the quote signature, the certificate chain, and validating measurements against known-good values, often via reproducible builds and binary transparency logs.A key challenge arises from the trust model clash: MPC decentralizes trust, while TEEs centralize it in the hardware manufacturer. TEEs also invert traditional security, trusting the guest code while considering the host untrusted, introducing new attack surfaces like rollback attacks. While TEEs can mitigate issues like ambiguous encoding, misbehaving participants, missing parameters, and missing input validation by ensuring protocol compliance through attestation, they do not guarantee perfect security.Real-world TEE implementations have vulnerabilities, and attestation processes can be incomplete or incorrectly verified. A common pitfall is incomplete attestation measurements, where critical components are excluded, allowing undetected modifications. Another issue is missing verification steps, such as not checking the quote signature or certificate chain, which breaks the security model. These issues underscore the need for rigorous implementation and verification practices when combining TEEs with MPC.