Google Cloud Blog
Follow
Empowering autonomous agents with advanced security governance
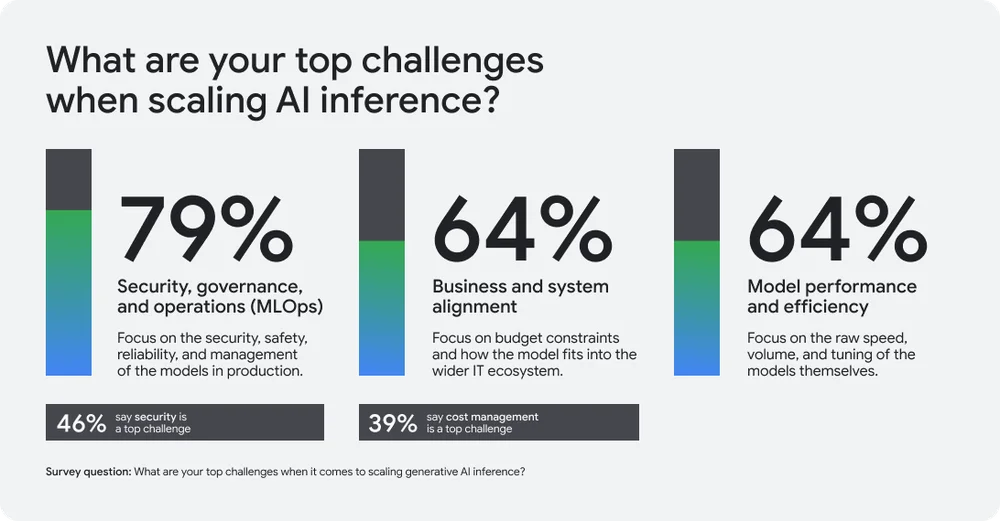
AI agents, with their access to sensitive data and ability to trigger actions, present both opportunities for productivity and significant new security challenges. A vast majority of tech leaders identify security and governance as major hurdles to scaling AI inference. Traditional security models are insufficient due to the fundamentally altered threat landscape introduced by autonomous workflows. Granting agents necessary access while maintaining security is a complex balancing act, often referred to as the "agentic paradox." Insufficient security for multi-system agent access is a core concern preventing wider deployment. Agents expand the attack surface and introduce novel threats like tool poisoning and indirect prompt injection. Securing agents requires a shift from solely breach prevention to verifying data provenance. Organizations are increasingly adopting full-stack cloud platforms to gain oversight and manage risks, with data compliance being a primary driver. Frameworks and purpose-built platforms enable secure-by-default design, robust agent governance, and human-in-the-loop control for critical actions. Ultimately, strong governance integrated into a unified security foundation allows organizations to deploy agents confidently and innovate securely.