Google Cloud Blog
Follow
How Blackline simplifies perimeter policy intelligence with VPC Service Controls
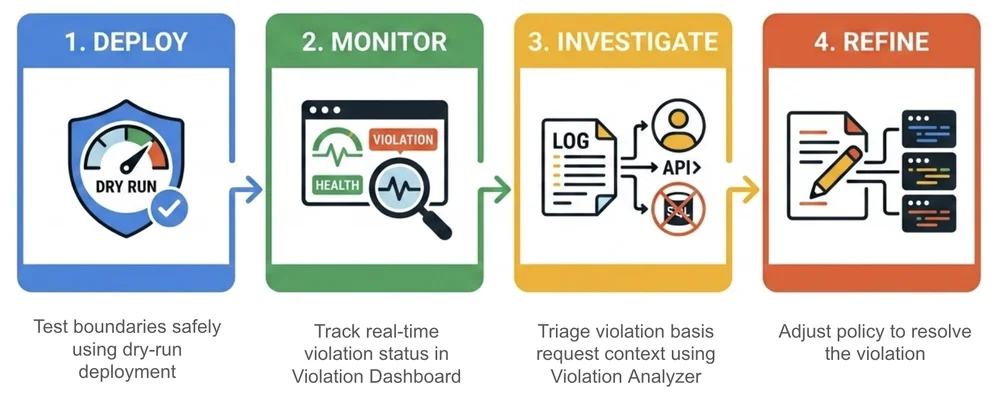
VPC Service Controls are crucial for protecting cloud environments from data exfiltration and other threats. Google Cloud has introduced new policy intelligence capabilities to simplify VPC-SC management and troubleshooting. These new tools include a violation analyzer and a violation dashboard. Financial operations leader BlackLine uses VPC-SC to secure sensitive customer data and mitigate risks. The violation analyzer helps BlackLine administrators adapt security perimeters by identifying principals and resources involved in API request violations. Previously, resolving these violations required complex Cloud Logging queries, but the new tools provide detailed reports directly. The violation dashboard aggregates all service perimeter violations across an organization for trend identification and filtering. The violation analyzer streamlines investigations by mapping denials to specific rules without manual log analysis. These tools simplify the entire VPC-SC lifecycle, from testing new perimeters to refining policies and resolving incidents efficiently. By leveraging these advancements, organizations can spend less time on investigations and more time scaling their cloud initiatives securely.