Google Cloud Blog
Follow
Investigating Ephemeral Supply Chain Tampering
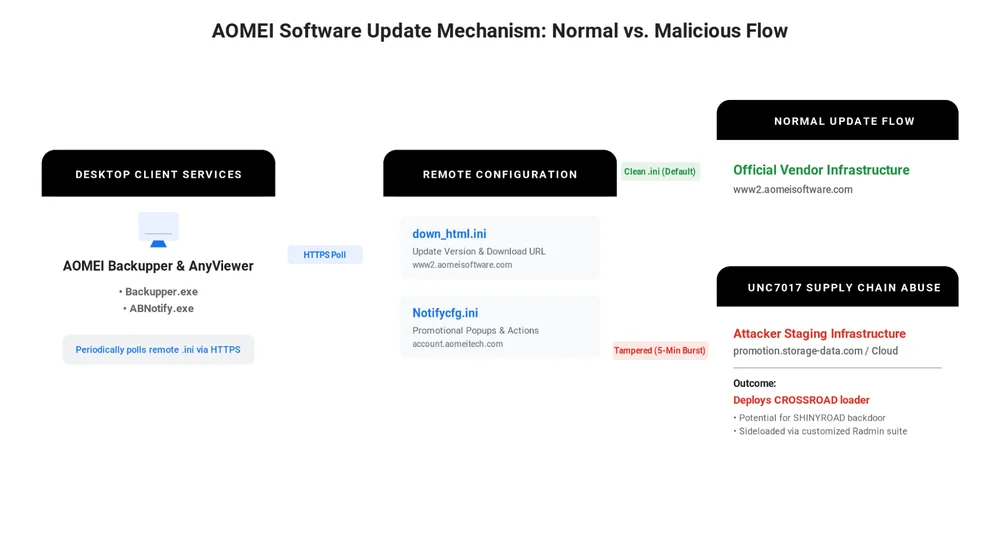
Google Threat Intelligence Group and Mandiant investigated a software supply chain attack against AOMEI Technology. The threat actor, UNC7017, repeatedly tampered with AOMEI's update servers in very short windows of five to ten minutes. This tactic was designed to evade traditional security detection methods. The campaign delivered a multi-stage payload, including the CROSSROAD downloader and SHINYROAD backdoor. UNC7017 strategically shifted its infrastructure from cloud providers to dedicated domains and cloud storage. Organizations across various sectors in multiple countries were impacted by this opportunistic campaign. The ManagedEngine Threat Analysis Lab (METAL) initially detected the activity through their EDR telemetry. GTIG subsequently notified affected organizations and shared findings with AOMEI, who then took corrective actions. The attack exploited AOMEI's update and notification logic by modifying configuration files like down_html.ini and Notifycfg.ini. UNC7017 also used a silent WebDAV credential coercion technique with an invisible popup. Malware delivery involved custom loaders and post-exploitation frameworks, including a modified Radmin Server backdoor. The CROSSROAD downloader validated the environment, cleaned endpoints, staged secondary payloads, and established persistence.