Planet Python
Follow
Peter Hoffmann: Home Server Ops with a Read-Only Agent and pyinfra
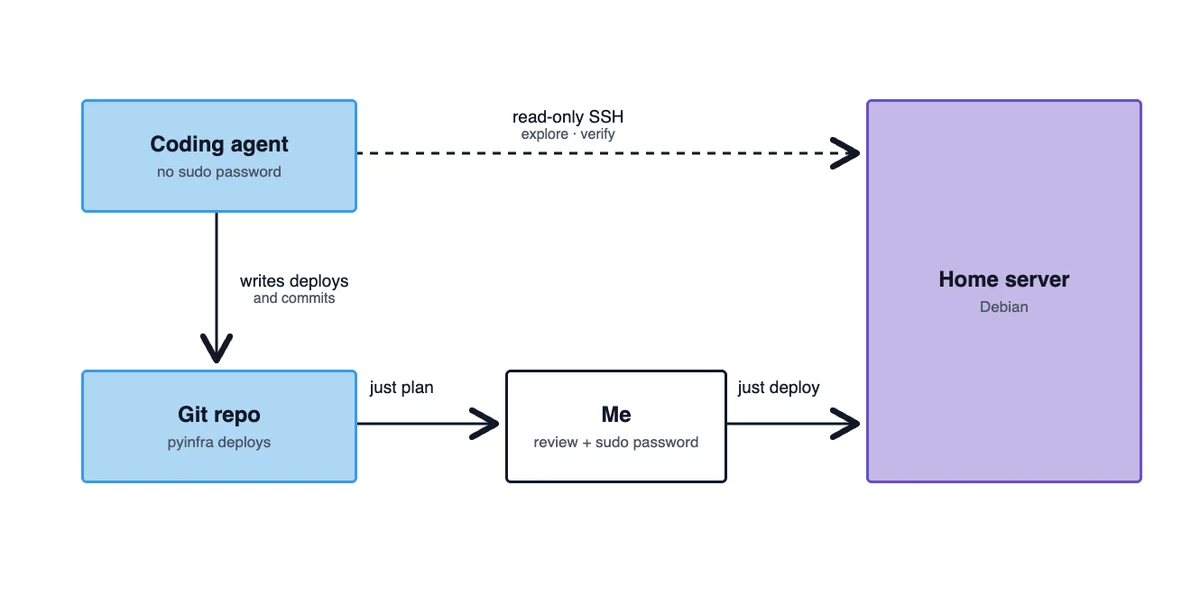
A home server, initially managed manually, was transformed using a coding agent and declarative configuration. This agent has read-only access, preventing direct server modifications. All changes are now codified in pyinfra deploys within a git repository. The agent explores the server, writes Python code for desired state changes, and presents these changes for review. Crucially, the sudo password acts as a gatekeeper, requiring user intervention for any actual deployment. The repository structure includes agent rules, a server state inventory, pyinfra deploys, and configuration files. The agent's tasks include reading documentation, locating configurations, and writing systemd units. The user reviews dry runs and then executes the code for deployment. This workflow handles system upgrades, migrating services, and deploying custom applications. Mistakes are learned from and incorporated into agent rules for future sessions. While effective for personal data, read-only access requires consideration for machines holding sensitive third-party information.