Google Cloud Blog
Follow
Shutting the Door on the XCPE Botnet
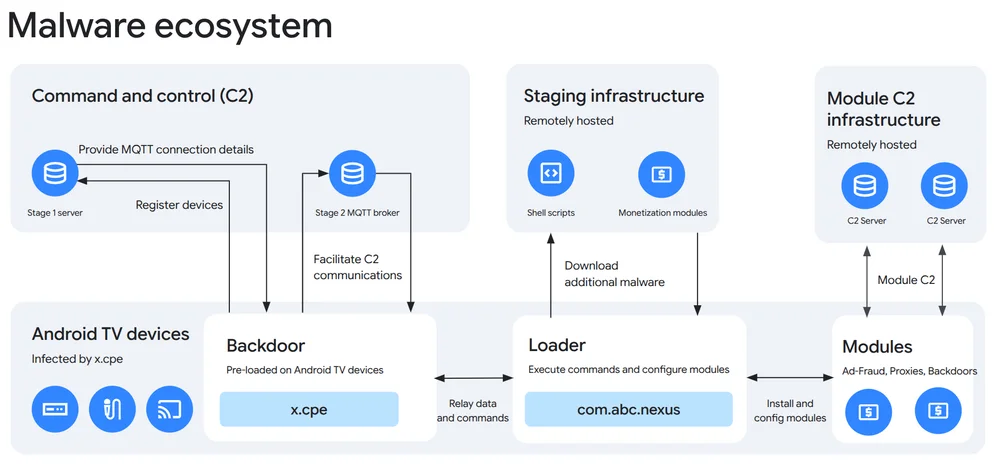
Google and partners dismantled the XCPE backdoor, a botnet of over 1.3 million set-top boxes. Videostrong Technology Co., an Android OEM/ODM, intentionally developed and operated it for financial gain. Videostrong monetized the backdoor by selling access to criminal affiliates, who loaded ad-fraud, residential proxy, and additional malware modules onto infected devices. Google has severed ties with Videostrong, banning them from making devices with preloaded Google apps. Videostrong exploited a gap in Google's compatibility tests using obfuscation techniques to load malicious code after device boot. Google implemented changes to its review process to prevent similar activity. This campaign was a serious breach of trust, enabling a wide array of criminal activities on user devices without consent. Google's disruption efforts included legal actions against C2 domains and server infrastructure used by Videostrong and its affiliates. The company also improved firmware integrity checks for certified Android TV devices. The XCPE botnet utilized a modular, three-stage architecture: a primary system-level backdoor (x.cpe), a loader and execution engine (com.abc.nexus), and various monetization modules. The botnet uses a two-stage C2 process involving HTTP requests for configuration and persistent MQTT connections for commands. This allowed for silent app installations, Google Play Protect disabling, arbitrary shell execution, screen captures, and network reconnaissance.